

Information Security
Information Security Policy
BenQ Materials has established a secure and trustworthy computerized operating environment to ensure the security of data, systems, equipment, and networks, as well as to maintain uninterrupted operations. (Fordetails, please refer to the Information Security Policy.) The ''Information Security Policy and Procedures'' were developed in accordance with the Cybersecurity Management Act, Personal Data Protection Act, Copyright Act, Electronic Signature Act, and based on international information security standards such as ISO 27001. All employees, temporary staff, visitors, and vendors conducting business with the Company (including their employees and temporary staff) were required to comply with this policy when maintaining, safeguarding, using, or managing the Company's assets.
Information Security Management Policy:
- Strengthen the company's information security management to establish reliable information application systems.
- Protect electronic information assets to prevent and mitigate business losses.
- Enhance business interests and ensure sustainable corporate operations.
Information Security Management Objectives:
- Protect the security of the company's information services and ensure that information is only accessible to authorized personnel to maintain confidentiality.
- Protect the security of the company's information services by preventing unauthorized modifications to ensure accuracy and integrity.
- Establish a business continuity plan for information services to ensure uninterrupted operations.
- Ensure that all company information services comply with relevant laws and regulations.

Information Security Management Committee Organizational Chart
In 2021, BenQ Materials established the Information Security Management Committee and appointed a Chief Information Security Officer (CISO) along with an Information Security Representative (Dedicated Security Manager) to strengthen its information security management framework. To respond to evolving cybersecurity trends and comply with policies set by the Financial Supervisory Commission, the Company holds at least one annual review meeting on information security management. In 2023, the role of CISO was officially instituted. In April 2024, the Company further enhanced its cybersecurity governance by expanding the organizational structure of the IT department into the Digital Technology Center and establishing a dedicated cybersecurity unit - Information Security Section. This section is staffed with a dedicated security manager and two additional full-time security personnel, totaling three members. It operates under the Digital Technology Center and also encompasses the Smart Application Division, the Machine Vision Division of the Machine Intelligence Division, and the subsidiary.

Information Security Management System
To ensure proper protection of information assets, BenQ Materials implements risk assessment procedures, establishes and enforces relevant regulations to determine the risk level of its information assets. Based on the results of these risk assessments and internal meetings, the Company determines appropriate treatment measures—such as risk mitigation, transfer, elimination, or acceptance—to effectively manage risks. BenQ Materials’ Taoyuan Headquarters, Longtan Plant, and Yunlin Plant obtained ISO 27001 certification, 2013 version, in 2021. To make information security management more comprehensive, the Company introduced certification under the new version of ISO 27001 (2022 version) in 2024 and passed certification in 2025. The certificate is valid from April 1, 2025 to March 31, 2028.
The scope of the ISO 27001 certification covers Taoyuan Headquarters, Longtan Plant, Yunlin Plant, ERP, the FEOL MES (Front End of Line Manufacturing Execution System), and the FlowER (BPM) system in Taiwan. In addition to the aforementioned server rooms and systems, the Suzhou Plant and Wuhu Plant in mainland China are also included in the management scope. In 2024, the Company planned to further extend management to the Smart Application Division, the Machine Vision Division of the Machine Intelligence Division, and subsidiaries with reference to ISO 27001 principles.
In 2025, BenQ Materials joined the cybersecurity governance structure of its parent company, Qisda, and complied with the corresponding security requirements. A cybersecurity maturity rating system has been established, and BenQ Materials, including its affiliated subsidiaries, is required to meet the parent company's cybersecurity evaluation standards, with continuous efforts made each year to enhance cyber resilience.
Information Security Risk Assessment
BenQ Materials, in accordance with its Information Security Risk Assessment and Management Procedures, defined the risk levels for Taiwan and Mainland China in 2022 and developed improvement plans for high-risk items. In 2023, the Company conducted a reassessment of the information security systems in both Taiwan and Mainland China, completing the evaluation in the third quarter. Two higherrisk issues were identified and incorporated into the Company's risk management operations, with improvement plans initiated in 2024.
In 2025, the Company continued to strengthen information security and operational resilience, with a focus on enhancing business continuity and disaster recovery capabilities for critical systems to ensure service stability; improving the incident classification, reporting, and decision-making governance mechanism for information security events; promoting consistent implementation of risk assessment and control measures between the parent company and subsidiaries; continuously inventorying and improving the risks of end-of-service (EOS) information equipment.
Information Security Management Measures
Hardware Protection
- Equipment Inspection: Maintenance contracts are signed with vendors for important systems and equipment, with cybersecurity clauses incorporated into the contracts to ensure equipment updates and vulnerability patching. Equipment status is inspected regularly.
- Establish Data Backup Mechanism: A backup system has been set up, performing daily backup operations for servers and databases. In addition, a high availability (HA) mechanism has been established for important equipment.
Network Security Protection and Monitoring
BenQ Materials has established the ''Website Information Security Management Inspection Guidelines.'' Since 2021, the Company has conducted vulnerability scans and remediation for key system hosts and websites. In 2025, the scope of scanning was further expanded by increasing both the number and frequency of scans on network devices and system hosts to enhance overall system security strength.
Information Security Incident Response Plan
Annual Disaster Recovery Drills: In 2024, BenQ Materials conducted a disaster recovery drill for the shipping cycle system to strengthen its disaster response capability and minimize potential losses in the event of an incident.Information Security Education and Training
- Relevant cybersecurity early warning equipment and mechanisms have been introduced to visualize internal security risks that were previously opaque. By integrating external cybersecurity intelligence and analysis, the Company can identify external hacker intrusion behavior in advance and take early countermeasures. Protect the security of internal corporate data and systems.
- Internal and external vulnerability scans are conducted regularly, and vulnerabilities are proactively patched to reduce information security risk exposure .
- Outside-in penetration testing drills are conducted to perform in-depth vulnerability testing and analysis, identify potential risks in equipment and systems, and improve security.
- Join the Taiwan Computer Emergency Response Team Coordination Center (TWCERT) in 2023 to participate in collaborative defense operations.
- From 2024 to 2025, the Company expanded the breadth of early warnings.
Social Engineering Drills
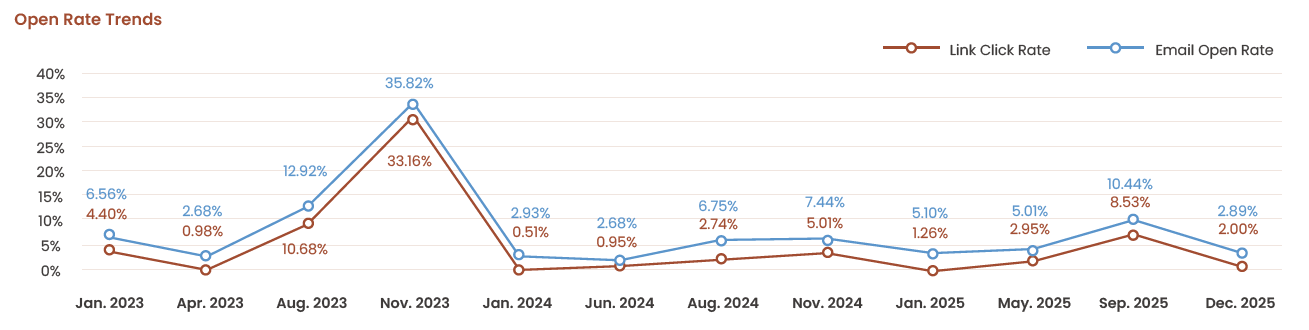
Since April 2021, the Company has conducted monthly email social engineering drills and provided employees with information security training on email sending and receiving to reduce the risk of employees mistakenly clicking malicious emails and strengthen email security awareness. Through continuous awareness promotion and staff retraining, the false-click rate continued to decline in Q1 2024.
In 2025, social engineering drills were enhanced by increasing the realism of the emails. In addition to including subsidiaries in the drills, the Company also adjusted the level of email simulation. Through continuous awareness promotion and staff retraining, the total number of participants for the year reached 4,068, with drills conducted quarterly. Email open rates ranged from 2.9% to 10.44%, and the average click rate was below 6.5%, meeting the strategic target.
Supplier Information Security Management
Each business unit ranked suppliers based on procurement amount and conducted a self-assessment for the top 10. A total of 71 suppliers were subject to self-evaluation. The cybersecurity self-assessment guideline uses a weighted scoring system based on performance in various areas, with suppliers categorized as follows:
Grade A+ (Excellent)
Supplier has a comprehensive and effectively implemented information security management system; weighted score ≥ 90%.
Grade A (Good)
Supplier has a well-established information security management system; weighted score ≥ 80%.
Grade B (Fair)
Supplier has a basic information security management system in place; weighted score ≥ 60%.
Grade C (Needs Improvement)
Supplier lacks an implemented information security management system; weighted score < 60%.
The overall average cybersecurity rating for 2025 was 76.85 points, categorized as Grade B (Fair), showing improvement from the previous year. Suppliers rated as Grade C (Needs Improvement) were provided with information security guidelines and recommended actions to strengthen their cybersecurity measures.
Supplier Information Security Evaluation
In 2025, an information security risk assessment was conducted for the top 10 suppliers of each product business unit, covering a total of 70 suppliers. The purpose was not only to provide an external risk reference for the Company but also to offer cybersecurity guidelines to suppliers to improve overall maturity and reduce potential risk exposure. The assessment results showed that 10% of suppliers did not meet information security control standards, defined as scoring below 60 points, resulting in an overall pass rate of 90%.
Cybersecurity Insurance Arrangement
Since December 2020, BenQ Materials has procured corporate cybersecurity risk insurance to cover expenses incurred from information security incidents, such as business interruption, incident response, and recovery costs. The coverage includes subsidiaries in which BenQ Materials holds a majority shareholding, thereby mitigating potential losses from security breaches.
In 2025, the Company continued its cybersecurity insurance coverage.
Information Security Personnel Training
Information security personnel actively participated in external seminars and completed more than 40 hours of cybersecurity training, including CYBERSEC Taiwan, Trend Micro product protection training, and other courses. They also continue to plan for international information security certifications, such as CISA, CEH, ISO 27001: 2022 Information Security Management System Lead Auditor, and IEC 62443- 2-1 Cybersecurity Management System Lead Auditor, to enhance professional competencies and keep abreast of key issues.
Employees are required to promptly report suspected information security incidents, vulnerabilities, phishing attempts or other suspicious activities to the Information Security Section or designated IT reporting channel. Reported events are assessed and classified by the information security team and escalated to the CISO and Information Security Management Committee according to their severity.